Inside NovuLabs, an
Enterprise Software House in Islamabad
A senior engineering team on a single mission: building mission-critical software that the world's most demanding institutions can trust.
Powering Critical Systems Globally
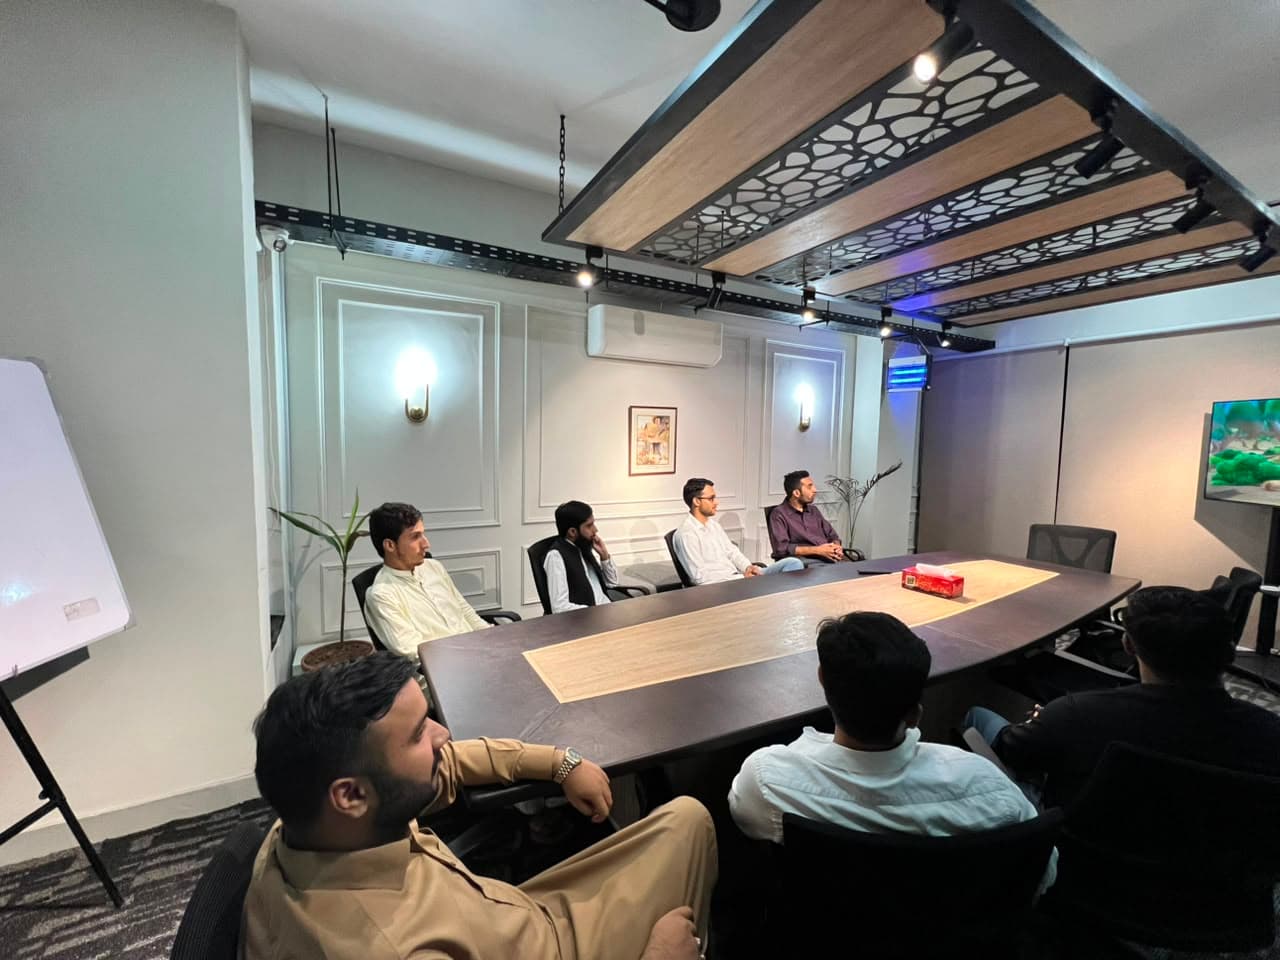
NovuLabs was founded in Islamabad by a senior engineering team with a single purpose: build software that matters. Not generic apps: mission-critical platforms that power financial systems, protect public health, and serve governments.
Our team brings deep hands-on expertise in fintech compliance, healthcare IT, and enterprise architecture, accumulated across years of delivering complex systems for regulated industries.
We measure success in transaction volumes processed, compliance standards met, and operations made more efficient through better software.
Mission-Driven
Every project starts with understanding what success truly means for your organisation.
Security-First
Security is the foundation of everything we build: from day one, not bolted on later.
Innovation
We adopt emerging technologies early, keeping our clients ahead of the curve.
Partnership
Long-term partnerships with shared goals and shared accountability, not one-off projects.
What engaging us actually looks like
Most software firms describe their process as a diagram with five arrows in it. That is not useful to somebody deciding whether to trust a supplier with a core banking integration or a hospital records platform. What follows is the actual shape of an engagement, including the parts that are uncomfortable to publish.
The first conversation is with an architect
There is no pre-sales layer here. The first call is taken by someone who would be accountable for the technical outcome, and it runs about forty-five minutes. That is a deliberate constraint on how we grow: it does not scale the way a sales team scales, and it means we talk to fewer prospects than we otherwise could. We accept that trade because the alternative; a commercial conversation that commits to an architecture nobody technical has examined, is how projects acquire the problems that surface in month five.
Expect that call to be diagnostic rather than promotional. The most valuable outcome is frequently a scoping correction: the thing you asked for is not the thing that solves your problem, or it is, but the sequencing is wrong.
We will tell you when not to build
A meaningful share of the enquiries we receive describe requirements that an existing product already meets. When that is the case we say so, and we say it before there is a proposal on the table rather than after. Recommending a custom build against a mature off-the-shelf product that fits just sells you maintenance liability at a premium.
The honest test is whether the requirement is genuinely differentiating. Payroll is not. Regulatory reporting against a schema your regulator controls, wired into a core system nobody else runs, generally is. We have written up the reasoning at length in our note on custom platforms versus off-the-shelf ERPs, including the cases where the answer goes the other way.
Compliance is designed in, not added on
In regulated delivery the expensive mistakes are almost never coding mistakes. They are architectural decisions taken early, without the compliance constraint in the room, that become structurally difficult to reverse once there is production data behind them.
Screening thresholds that were never governed. An audit trail that records the current state but cannot reconstruct what the system knew at decision time. A reporting pipeline built as an export at the end rather than as a schema contract at the centre. Each of those is cheap to get right at design time and expensive to retrofit, and each is the kind of thing an examiner asks about directly.
So the compliance owner is in the design sessions, not shown a demo at the end. This is the single practice that most distinguishes our delivery from a general software supplier taking on a regulated project for the first time. The detail is set out in our guides to AML/CFT architecture and goAML reporting pipelines.
Explainability over sophistication
There is constant commercial pressure to lead with machine learning in compliance and risk work. We push back on that for most institutions, for one specific reason: explainability is a regulatory requirement, not a preference. When an examiner asks why a transaction was or was not flagged, a model score is not a defensible answer.
The pattern we favour is layered: deterministic rules produce the decisions of record, and a model runs alongside to prioritise the review queue rather than to decide it. You get the analyst-efficiency benefit without putting an unexplainable artefact on the regulatory critical path. It is a less impressive slide and a considerably better system.
What we do not do
We do not take on work where the timeline only closes if testing is compressed, because in regulated systems the testing is the deliverable. We do not staff engagements with people the client has not met. We do not publish client names or logos without written permission, which is why our case studies describe institutions by category rather than by name; a constraint that costs us credibility with some buyers and which we accept, because the alternative is disclosing a client relationship somebody asked us to keep confidential.
We also do not claim certifications we cannot evidence. Where the site describes alignment with a standard, it means the engineering practice follows it, not that a registrar has audited us against it. Buyers in this market are asked to take a great deal on trust, and the least we can do is be precise about which claims are attestations and which are audited facts.
Where we work
The team is based in Islamabad (there is a fuller account of what we do as a software house in Islamabad, and of software development in Pakistan more broadly), and the regulatory environment we know best is Pakistan's; the State Bank's AML/CFT framework, the Financial Monitoring Unit's reporting requirements, RAAST, and the identity infrastructure that financial onboarding depends on. That depth is specific and hard to acquire remotely, and it is the reason institutions here come to us rather than to a larger generalist.
We also deliver into healthcare and public-sector programmes where the constraints are structurally similar even when the regulator is different: HIPAA safeguards and HL7 FHIR interoperability follow the same discipline of designing for audit from the outset. If you are evaluating us for work outside these areas, the useful first question is whether your problem is shaped like a regulated one. Frequently it is, and the reasoning transfers.
Read more about the people doing this work on our team page, the problems we take on across regulated industries, or the specific engineering services we deliver.
Frequently asked questions
Where is NovuLabs based?
What kind of projects does NovuLabs take on?
Do you work with clients outside Pakistan?
Who takes the first call?
Will you tell us if we should not build custom software?
Is NovuLabs ISO 27001 or HIPAA certified?
Question not answered here? Book a technical consultation; it is taken by an architect, not a salesperson.